Supervisors expect documented, risk-based oversight of your vendors. Galink gives you the process, the evidence and the dedicated registers.

They trust us in Europe and North America
Your challenges
The supply chain is now in scope
Under NIS2, vendor security is part of your cybersecurity risk-management measures.
Every step must leave a trail
Assessments, reassessment deadlines and remediation must all be traceable.
Dedicated reports
DORA, NIS2 and CS&R require you to document your arrangements with vendors and be able to share them with supervisors.
How Galink helps
A risk-proportionate approach
Criticality, calculated from your criteria, drives assessment rules, reporting and reassessment deadlines.

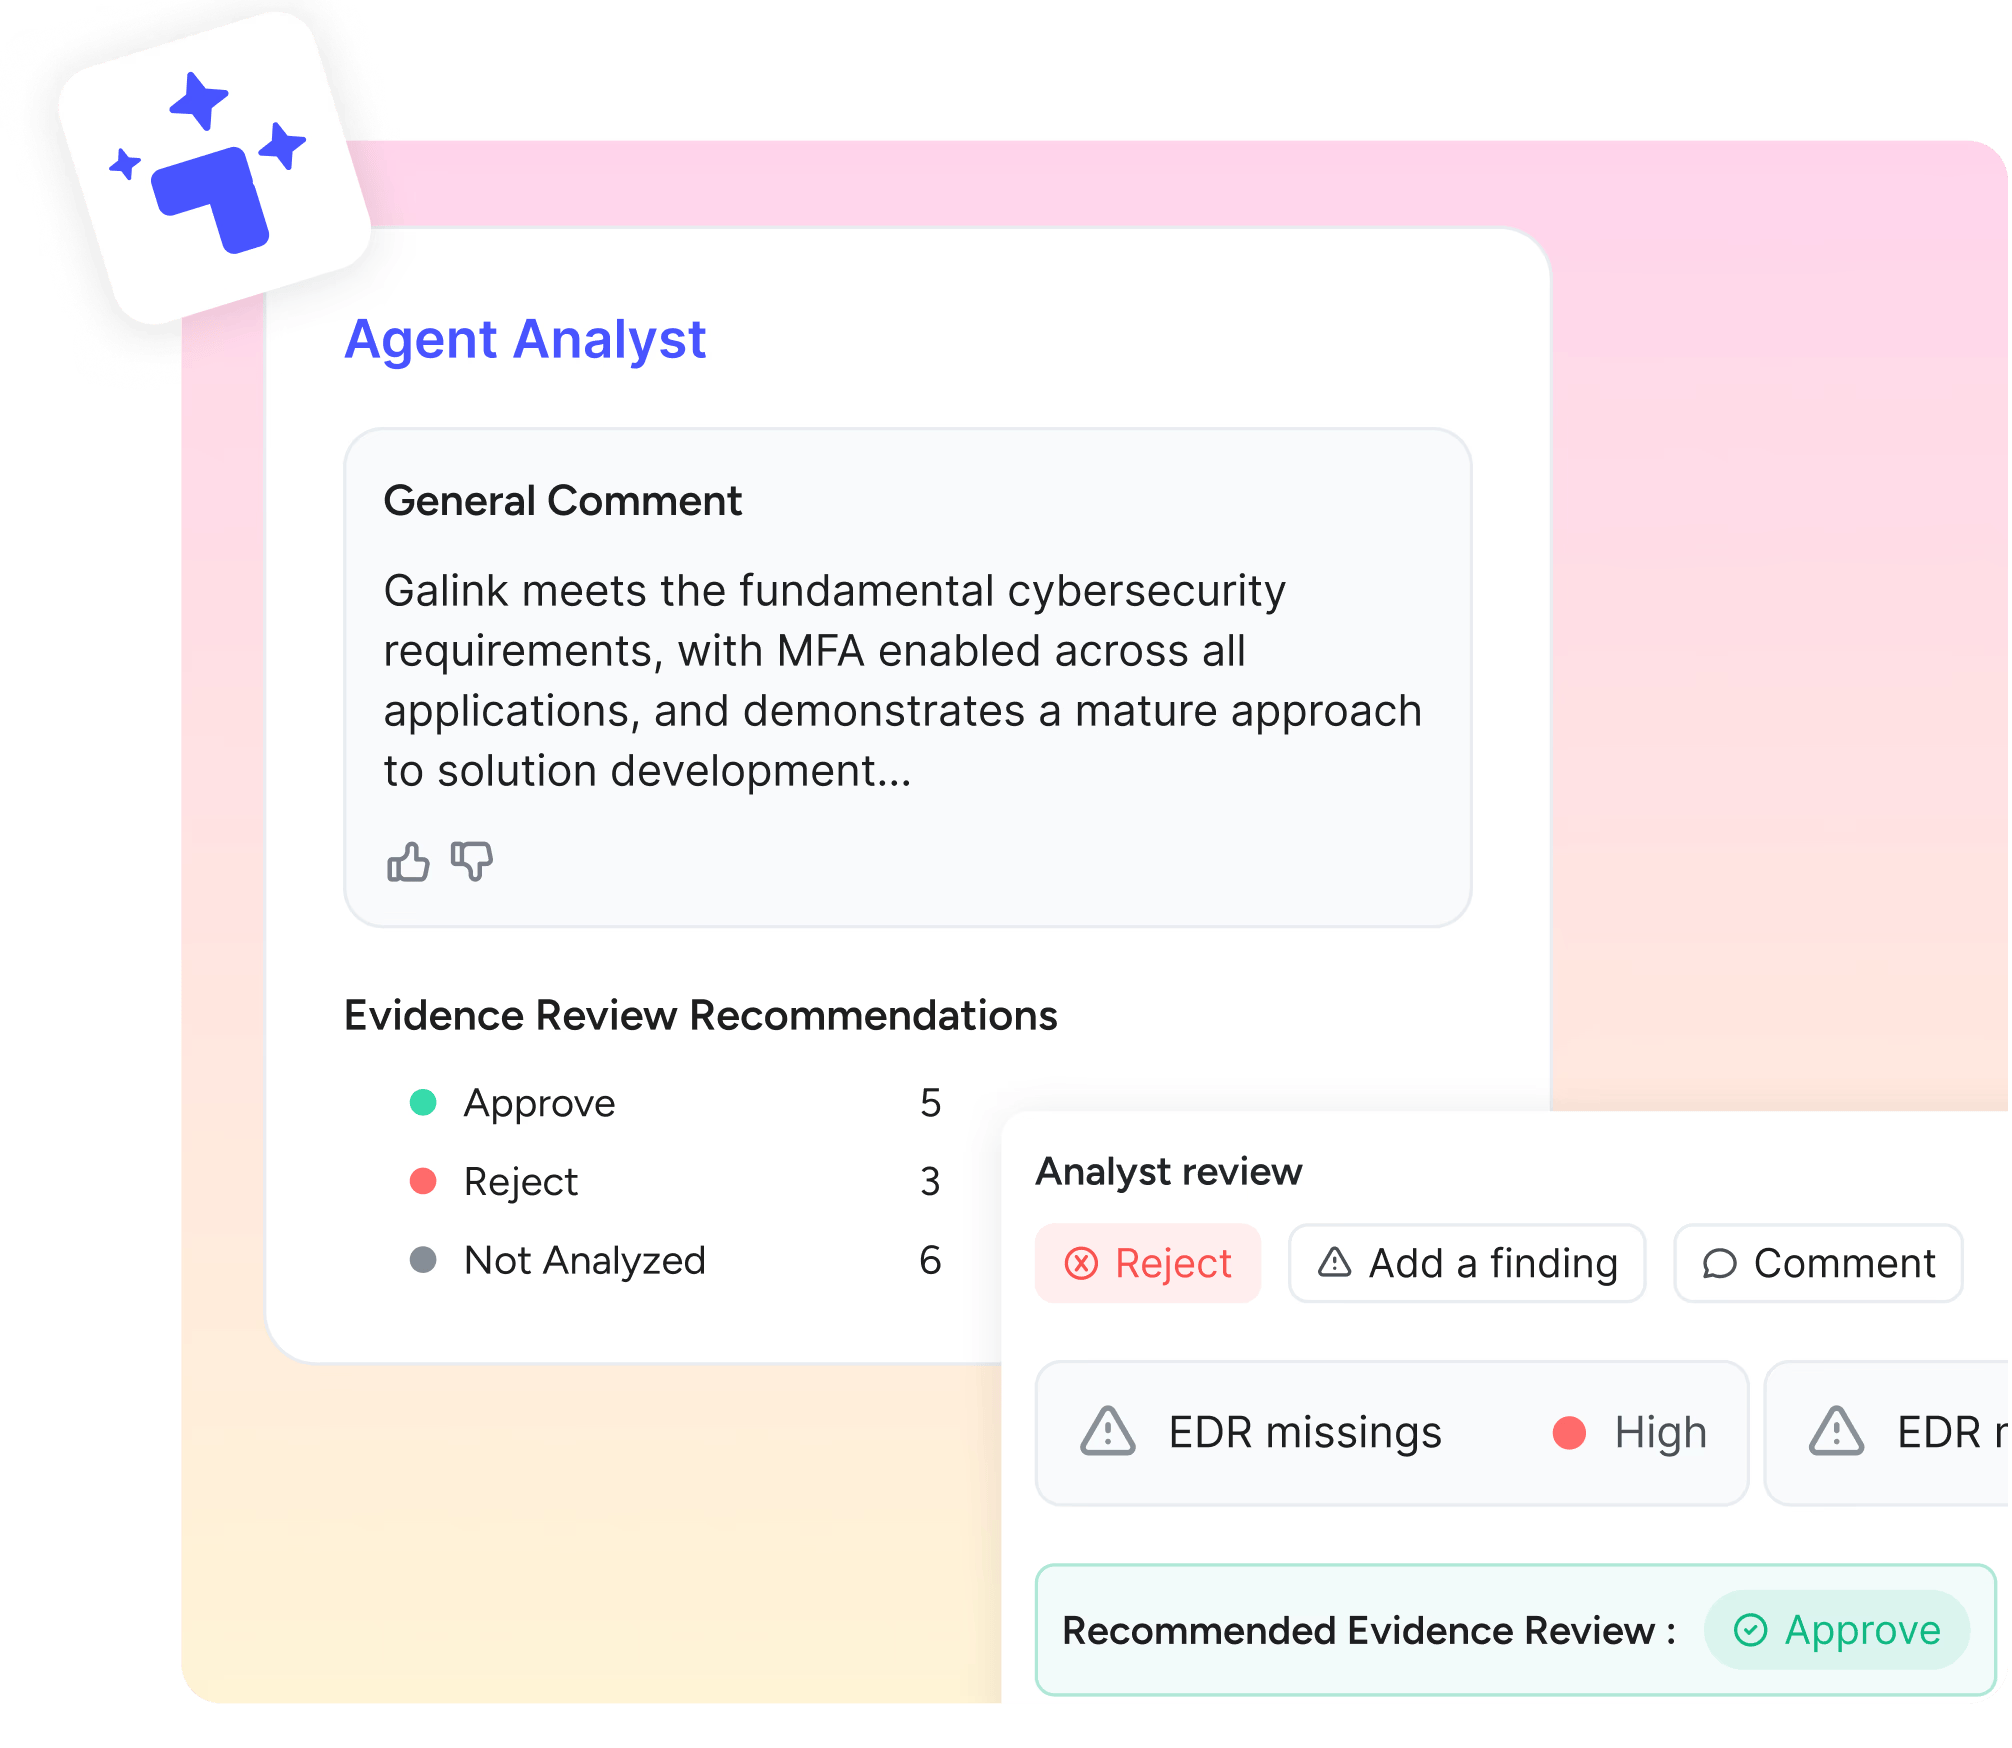
Evidence an auditor can follow
AI reviews evidence against your criteria: scope, pentest findings and ISO certificate validity. Questionnaires keep their version history and remediation is tracked to resolution.
See Seel in action
Seel runs assessments end to end, and every step is logged: questionnaires, evidence analysed, follow-ups and decisions.
Proven results
100+
client organizations, primarily in banking and insurance
ISO 27001
Galink is certified
5 to 10x
less time per vendor assessed

“Galink fits perfectly into our DORA and CRA compliance approach. We now build vendor cyber risk assessment directly into project workflows instead of handling it after the fact. Security by design is becoming a reality.”
CISO
Retail · 10,000 employees