
DORA, CS&R and your supervisors’ expectations covered in a single platform: traceable assessments, tracked remediation and an up-to-date Register of Information (add-on).
They trust us in Europe and North America
Your challenges
Hundreds of ICT providers
From critical cloud services to niche software vendors, every vendor must be tiered, assessed and monitored.
Demanding supervisors
Every decision, reassessment deadline and remediation must be traceable.
A DORA register to maintain
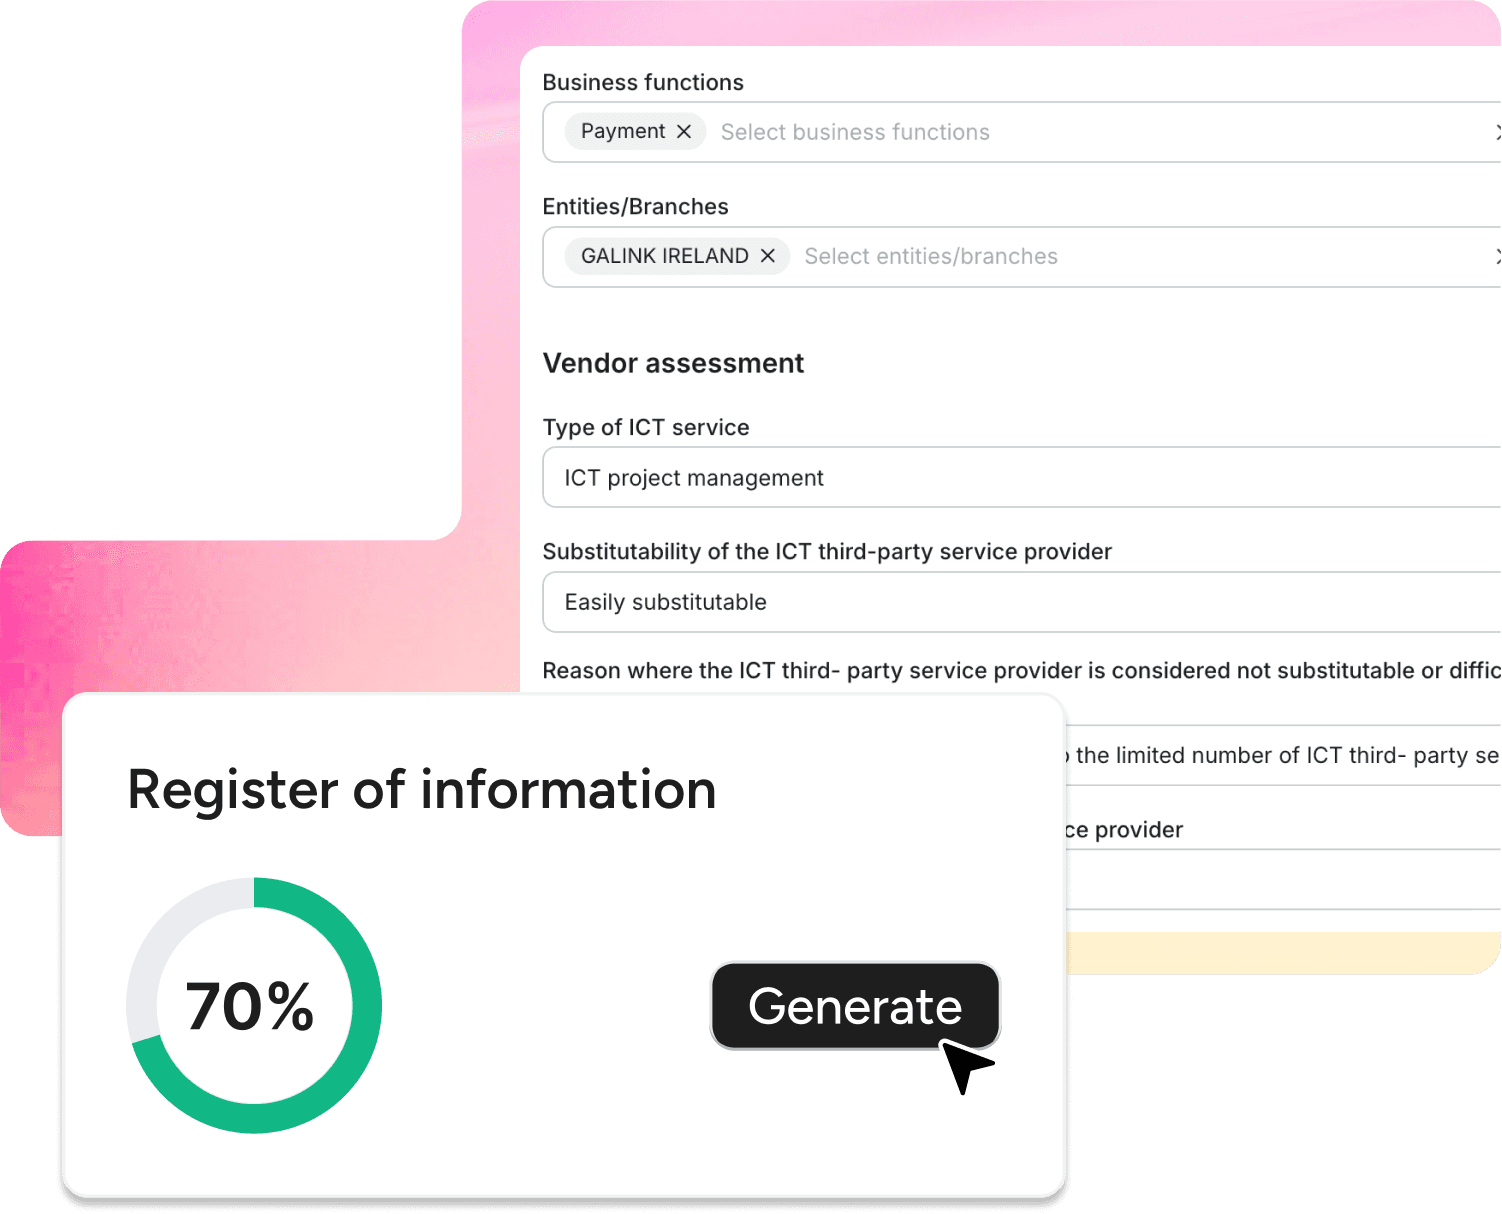
The Register of Information must be documented, kept up to date and ready to submit to supervisors.
How Galink helps
Built around DORA
The criticality of each ICT provider, calculated from your criteria, sets assessment rules and reassessment deadlines.


Evidence an auditor can follow
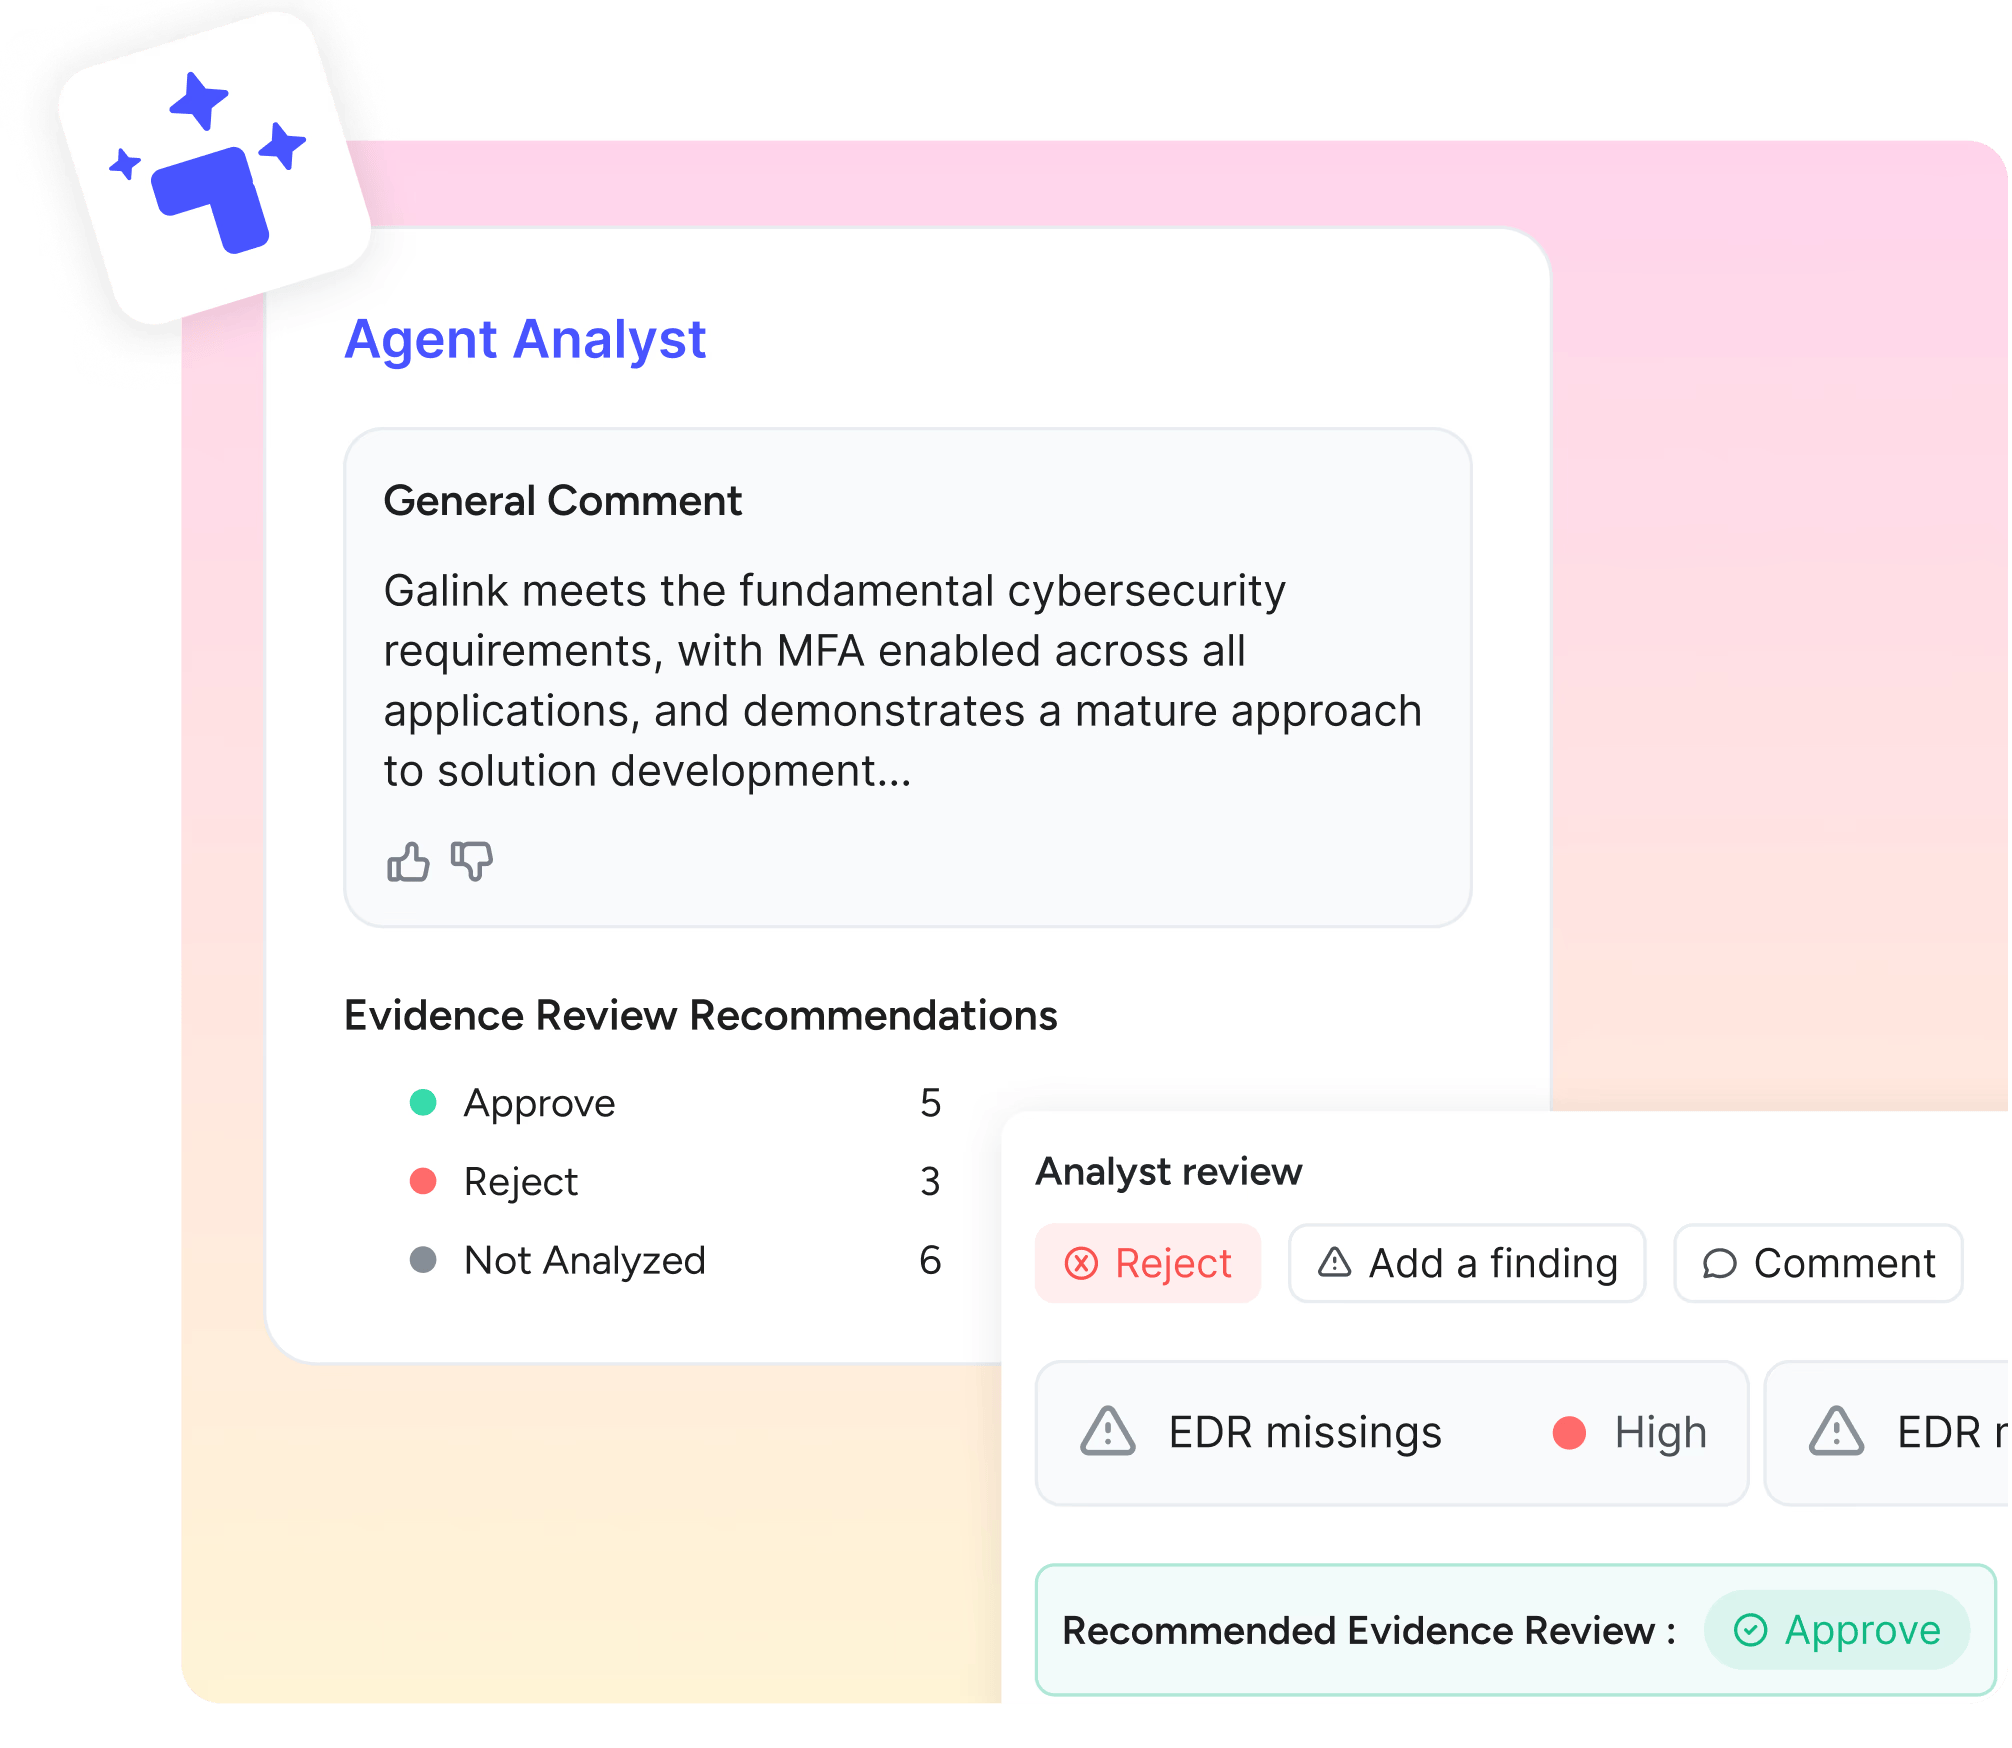
AI reviews evidence against your criteria: scope, pentest findings and ISO certificate validity. Questionnaires keep their version history and remediation is tracked to resolution.
Group-wide deployments
Multi-entity and multi-country, with our analysts as backup to assess your vendors against NIST and ISO 27001.

See Seel in action
Seel sends questionnaires to your ICT providers, analyzes answers and evidence, and follows up until they are complete. Every step is logged.
DORA Module
Your information registry, with no need for re-entry
1
You are sending your old register
Excel / CSV / extraction tool / even an "ugly" file.
2
We upload it, we clean it for you.
We manage the fields, duplicates, formats, links, and inconsistencies.
3
You regain control in a simple UI.
Edit a line, add a vendor, export with one click.
Proven results
100+
client organizations, primarily in banking and insurance
ISO 27001
Galink is certified
1 000
cybersecurity professionals at the Vendor Risk Summit
“Before Galink, we were juggling spreadsheets and emails just to assess vendors. Now everything is in one solution. It’s probably the simplest and most effective setup I’ve used so far.”
CISO
Banking · 2,000 employees